Find the weakness.Fix the risk.
Vulnerability assessment, penetration testing, mitigation, and configuration review for teams that need clear evidence and a practical path to lower risk.
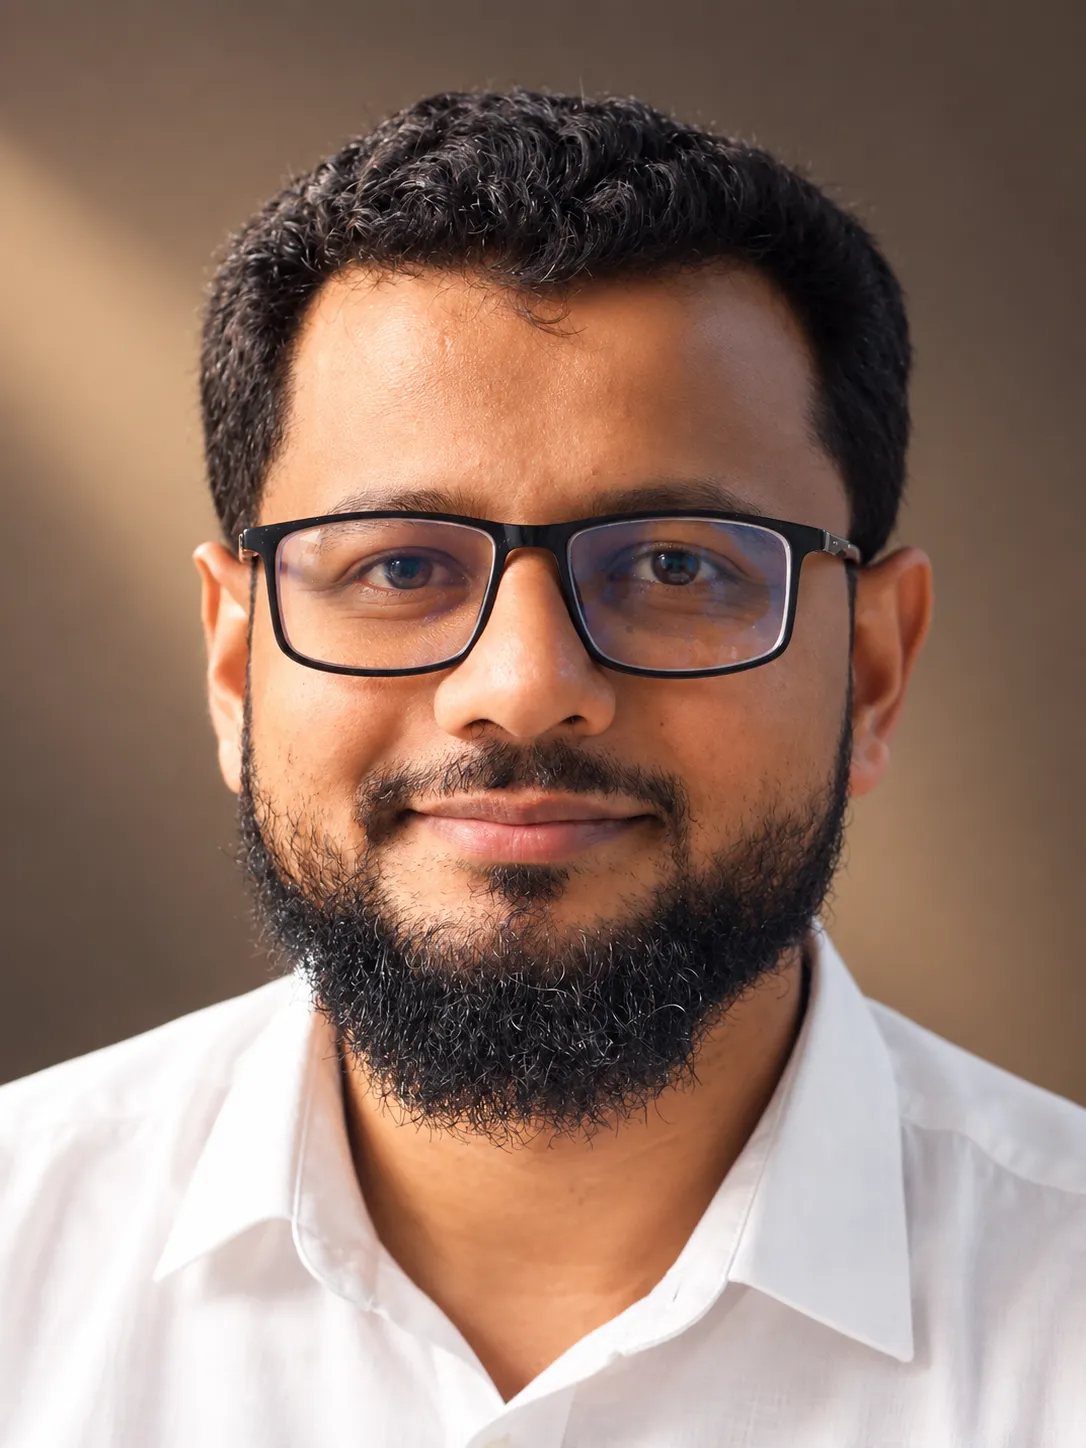
14+ years in network & system security
Selected security work
Four focused samples showing how I move from evidence to a practical security decision.
From scope to verified fix
A controlled workflow designed to produce evidence your technical team can act on.
- 01
Scope
Assets, objectives, access, testing windows, and rules of engagement.
- 02
Assess
Automated discovery plus targeted manual review.
- 03
Validate
Remove false positives and establish real business impact.
- 04
Remediate
Prioritized fixes with ownership, effort, and rollback awareness.
- 05
Retest
Verify the change and update the finding with evidence.
Grounded in established practice
What you receive
- 01Executive summary
- 02Technical findings with evidence
- 03Risk-ranked remediation plan
- 04Retest status
- 05Cleanup confirmation
Active testing begins only after written authorization and agreed rules of engagement.
Senior judgment. Usable evidence.
I’m Sakibur Rahman, a network and system security leader with 14+ years across enterprise infrastructure, SOC operations, cloud, and application security. I translate technical findings into remediation steps that infrastructure, development, and leadership teams can use.
- Network & System Security leadership
- Enterprise SOC implementation
- ISMS policy and ISO 27001 governance
- Security checks embedded across the SDLC
- LLM-assisted SIEM triage with Wazuh
Selected credentials
- ISC2 CISSPvalid through 2029
- ISO/IEC 27001 Lead Auditorvalid through 2029
- ISO/IEC 27032 Lead Cybersecurity Managervalid through 2029
- PECB Pen Test Professionalvalid through 2028
- Microsoft Cybersecurity Architect Expertvalid through 2028
- EC-Council Certified SOC Analystvalid through 2028
- Fortinet Certified Professionalvalid through 2027
- Certified Ethical Hackervalid through 2027
Selected toolkit
Nessus Burp Suite OpenSCAP BloodHound PingCastle Prowler ScoutSuite Wazuh FortiGate
Need a security finding you can act on?
Share the asset scope, objective, and preferred testing window. I’ll help define the right assessment.